
Automated awareness programs
An awareness program assigns cybersecurity content to the people in your organization across the year. SMARTFENSE brings them complete, one to three years long, and our content team keeps them up to date. You choose which one, when it starts and who it reaches.
Request a demo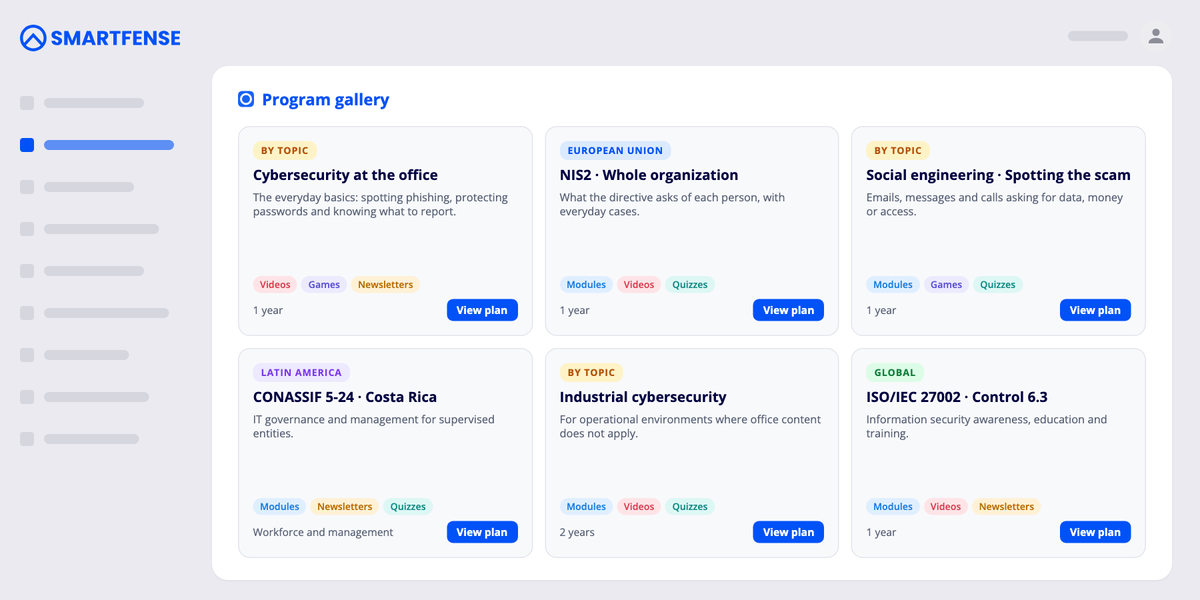
Almost every cybersecurity regulation asks for the same thing in different words. That people receive periodic training, and that you can prove it. None of them brings the syllabus.
Someone has to decide which topics go in, in what order, how long each stage lasts and what gets assessed at the end. That work is instructional design, it has little to do with information security, it takes weeks, and it has to be redone when the regulation changes.
Each program brings its full path: the content chosen, the order, and the time each stage takes.
NIS2, DORA, GDPR and the EU AI Act, among others.
The regulations of Argentina, Chile, Costa Rica, Ecuador, Paraguay, Peru and Uruguay, among others.
ISO/IEC 27002, PCI DSS and HIPAA, among other frameworks.
Industrial cybersecurity for operational environments, and general programs for starting without a regulation behind them, with different depth and time load.
The catalogue grows every time a new regulation appears, so the current list is always the one in the platform.
The catalog programs are fixed. The other format decides person by person.
Fixed program
You define the path once and it reaches everyone the same way. It is the format of the catalog programs, and it can be explained to an auditor in one line.
Smart Path
You define criteria instead of a path, and each person gets their own. It never repeats what someone already completed, and it stays within the monthly time you set.
You see what each person will receive, in what order and on what dates, once you choose the start.
The program plan, with the content of each stage and its dates.
It is the piece that gets the program approved inside the organization, and the one you use to agree with a client on what they will receive.
The difference matters when the audit arrives.
It covers the training and awareness requirement of the regulation, with per-person evidence of what was assigned and who completed it.
It does not cover technical controls, policies or security governance, and it does not replace your legal advisor’s judgment on how the regulation applies to you.
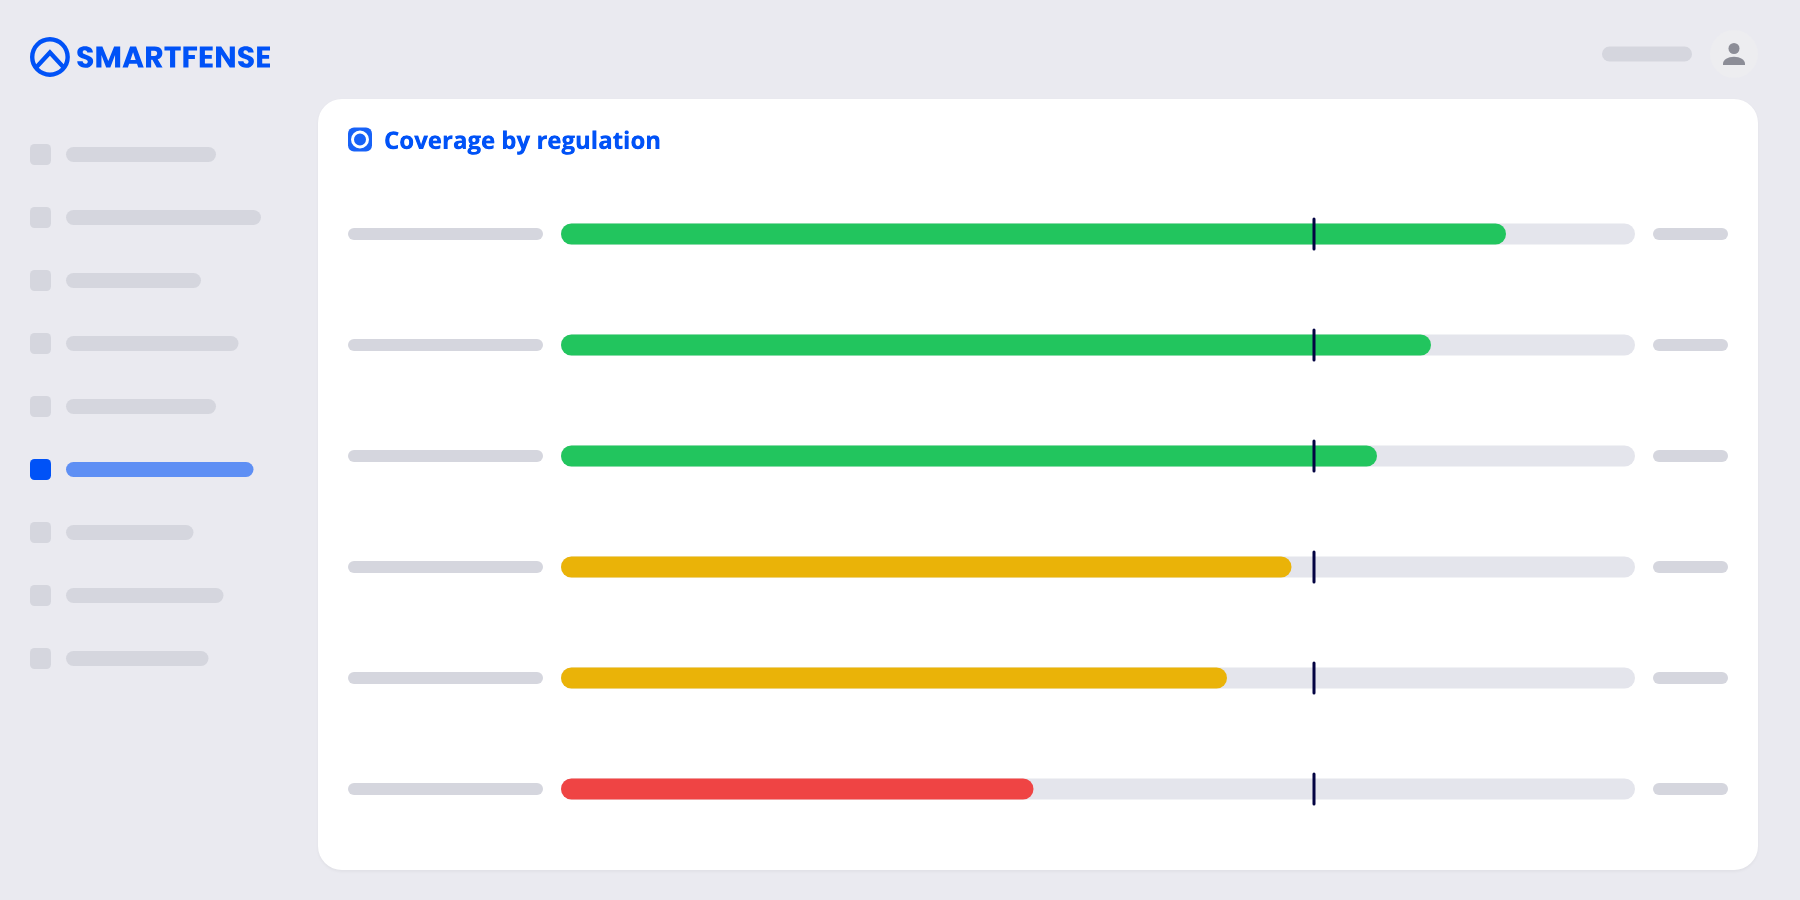
The coverage the program reaches in each framework, against the target you set.
Each framework has its own page, with the program mapped to what it requires on training.
European Union
The Latin American frameworks are covered too: the BCRA communications in Argentina, and the cybersecurity and data protection laws of Chile, Ecuador, Uruguay, Paraguay and Peru. You will find them in the compliance hub; those pages are in Spanish.
You can review the full list of regulations in the compliance hub.
+1,000
organizations run their awareness program with SMARTFENSE
The modules, videos, newsletters, exams and simulations the program assigns come from the SMARTFENSE catalog, and each format has its own page under cybersecurity awareness tools.
We will show you the gallery, the full plan of a program, and the evidence each send leaves behind.